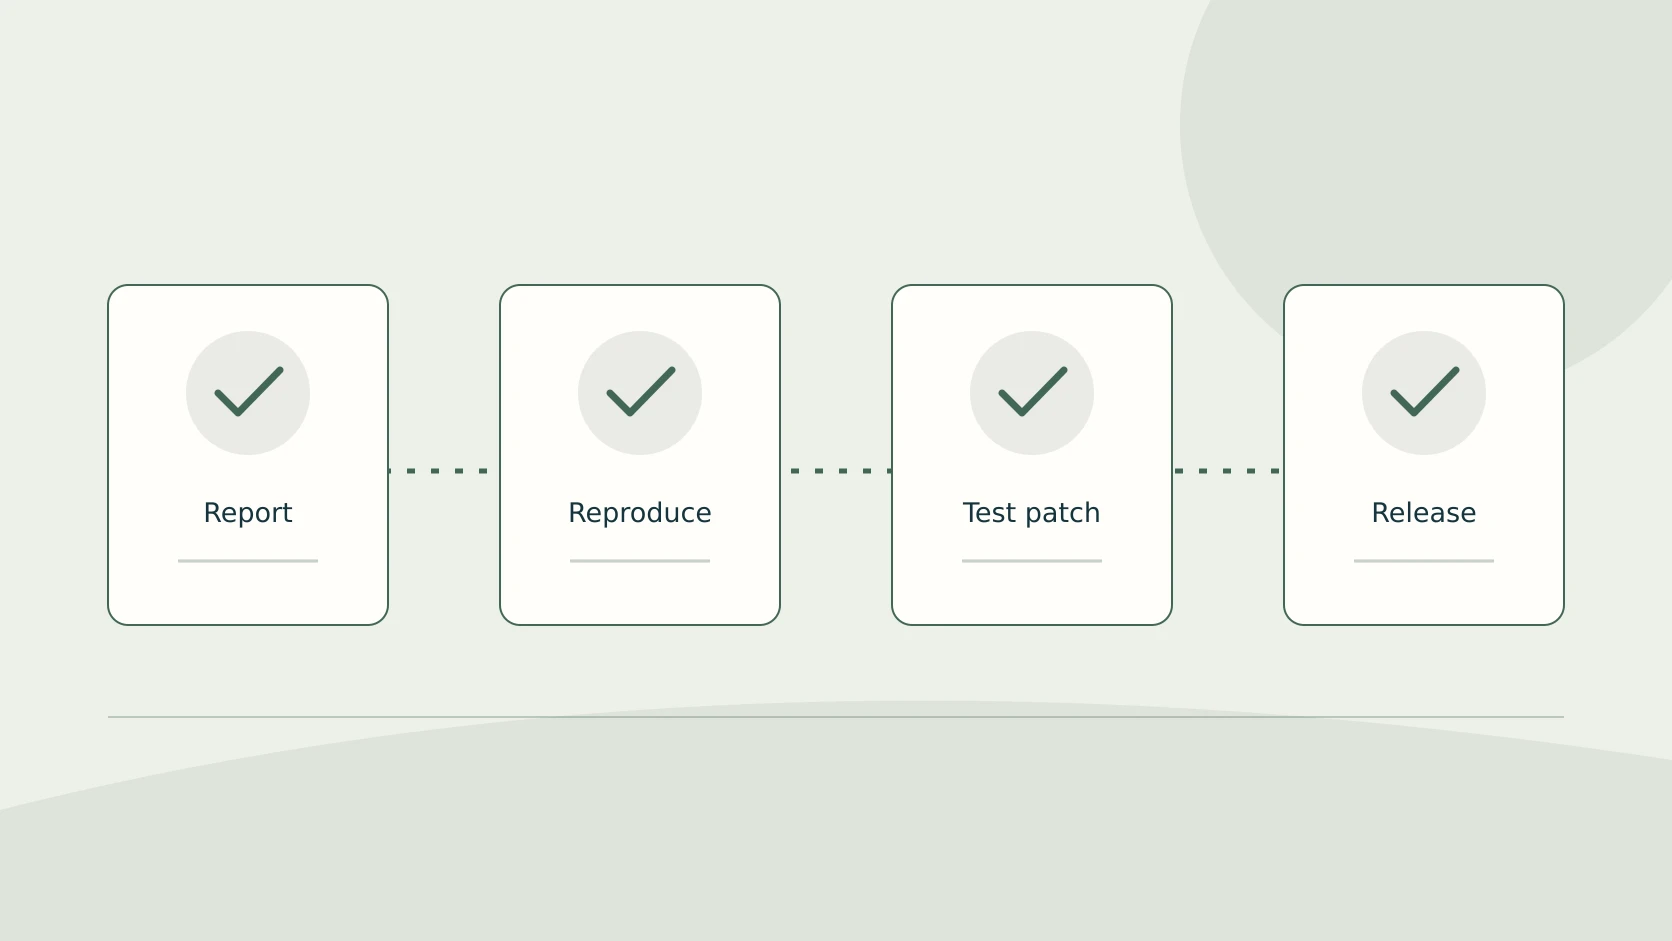
Anthropic launched an opt-in vulnerability-finding service on 8 October. Accepted open-source projects receive raw model reports; these are not human-validated findings. Maintainers must assess reports and candidate patches before acting.
RELATED BUYER PROFILEReview access, limitations and buyer evidencePricing · access · strengths · limitations →CONTINUE THE DECISIONCheck permissions and approval boundariesEvidence · workflow · next action →CONTINUE THE DECISIONBudget review and complete-work costEvidence · workflow · next action →What you need to know
- Anthropic launched an opt-in vulnerability-finding service on 8 October. Accepted open-source projects receive raw model reports; these are not human-validated findings. Maintainers must assess reports and candidate patches before acting.
- Confirm that a core maintainer controls the enrolment
- Confirm disclosure, pause and data-handling rules
Why it matters
Free scanning can still create a review workload. Decide who will reproduce findings, evaluate suggested changes and communicate confirmed vulnerabilities before enrolling a critical dependency.
Verified programme boundaries
The research announcement describes case-by-case admission for established projects important to infrastructure or user security. Reports may contain an explanation, reproducer and candidate patch. Anthropic separates this opt-in service from its continuing human-validated coordinated disclosure work.
Cyber Mission is a separate route
The 8 October Cyber Mission announcement also introduces a critical-infrastructure defence programme. That partner-led route should not be confused with the open-source scanning service or an entitlement to general model access.
Limitations and HubAI buyer verdict
Raw model output can be wrong. Supplier accuracy expectations are not a HubAI benchmark, and a suggested patch is not evidence of a secure release. Enrol only with a named maintainer and a manageable triage queue. Confirm current admission, disclosure and pause rules in the official service documentation. No UK-wide eligibility guarantee, public model API ID or independent HubAI Score is established here.
HUBAI VIEWRaw model output can be wrong. Supplier accuracy expectations are not a HubAI benchmark, and a suggested patch is not evidence of a secure release. Enrol only with a named maintainer and a manageable triage queue. Confirm current admission, disclosure and pause rules in the official service documentation. No UK-wide eligibility guarantee, public model API ID or independent HubAI Score is established here.
Buyer decision signal: Official announcement · 8 October 2026
What to verify next
1Confirm that a core maintainer controls the enrolment
2Name a triage owner and set review capacity
3Reproduce findings before classifying severity
4Test every patch against the project threat model
5Confirm disclosure, pause and data-handling rules
Read the evidence
Capabilities, availability and prices can change. HubAI keeps analysis separate from the underlying official material.
01Anthropic service announcement — 8 October 2026Open source ↗02Anthropic Cyber Mission — 8 October 2026Open source ↗03Official OSS Scanner documentation and enrolmentOpen source ↗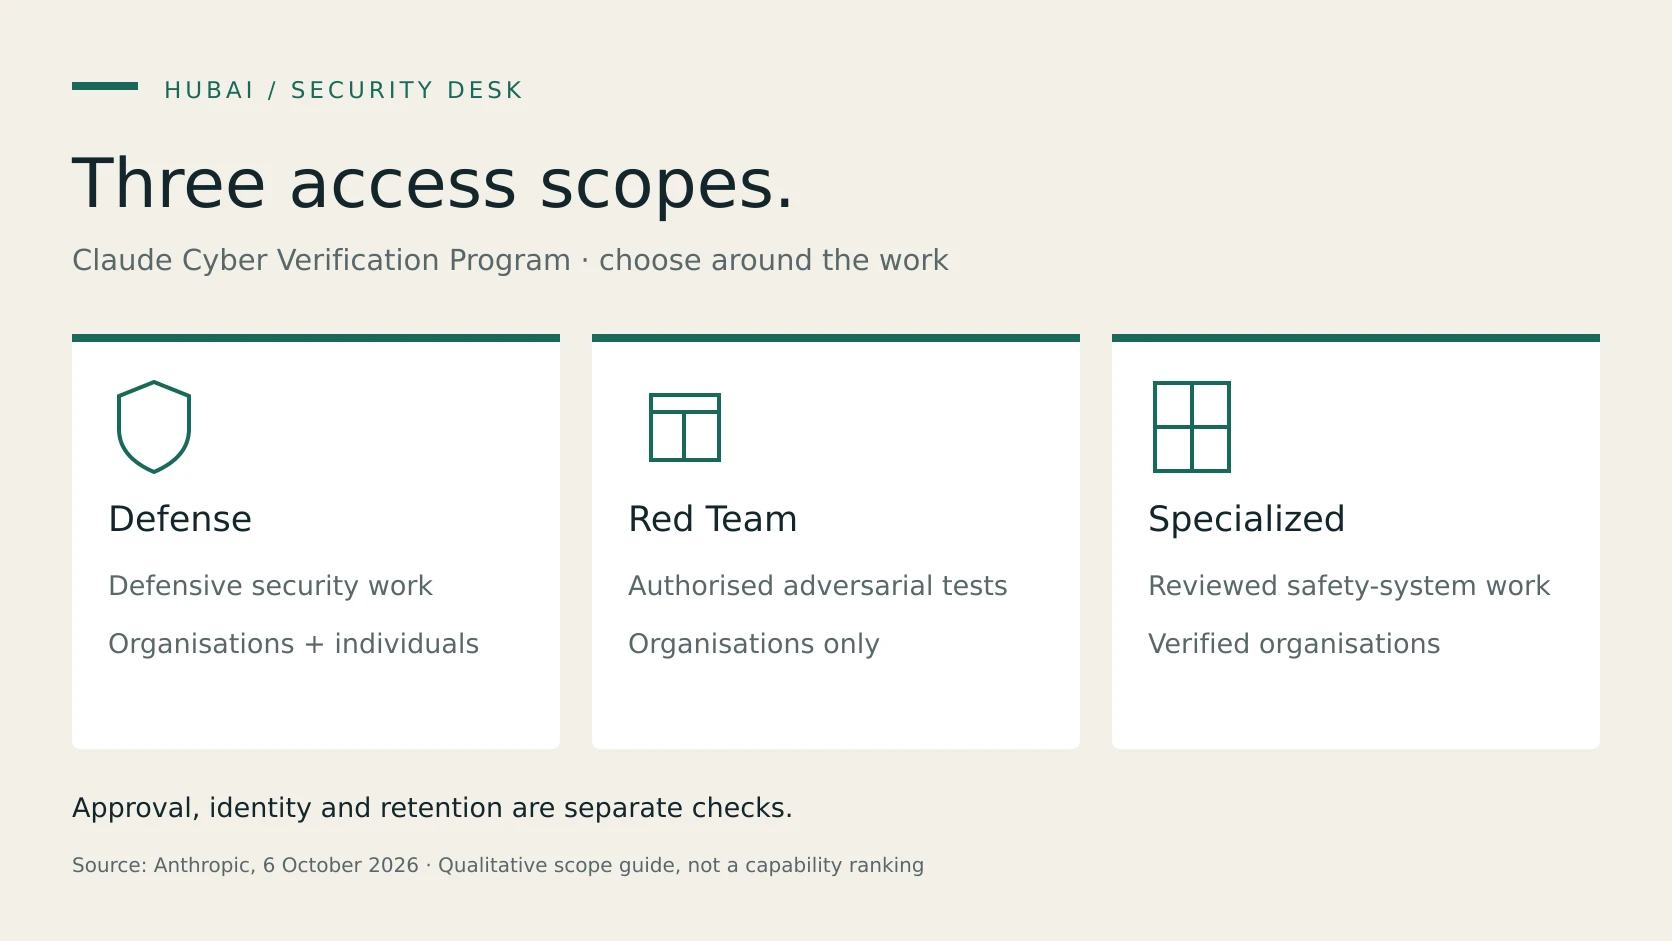 Safety
 Safety
 Safety
 Safety