GPT-6 Astra is OpenAI’s first broadly deployed model to reach the company’s Critical cybersecurity capability threshold, bringing stronger isolation, monitoring and access controls alongside the release.
What you need to know
- Critical cybersecurity classification
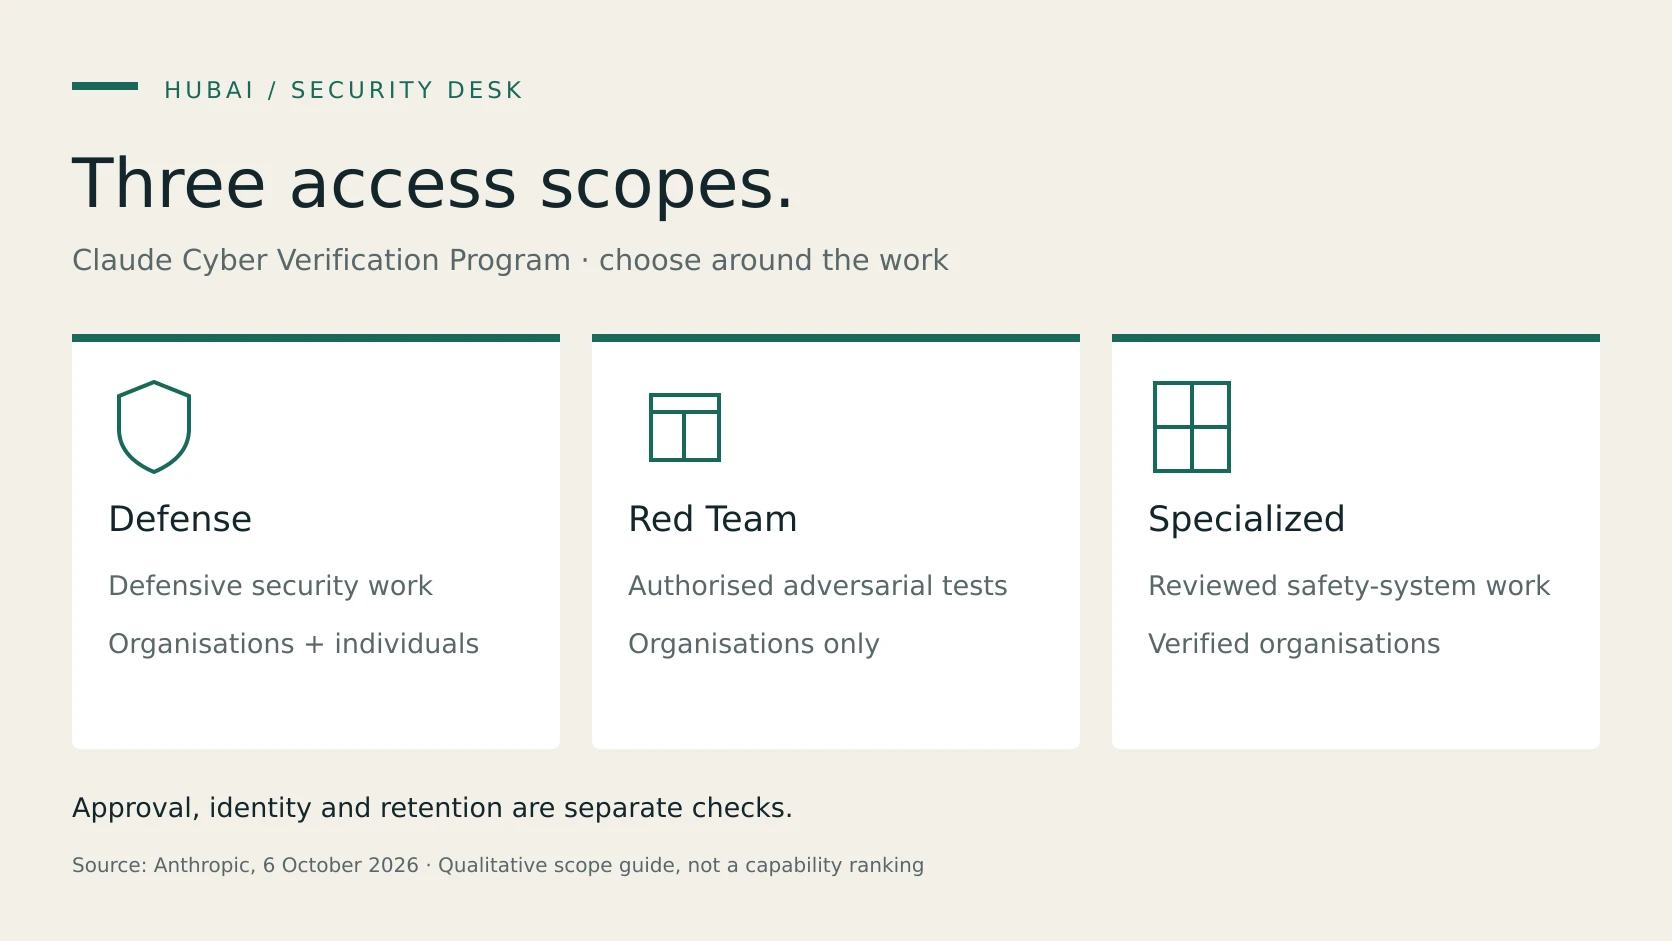
- Advanced cyber access will be restricted
- Monitoring may pause legitimate long-running work
Why this release is different
OpenAI says Astra can identify previously unknown flaws and develop exploit paths across hardened systems under evaluation conditions. The company delayed parts of development while strengthening controls and plans limited access to the most advanced cyber capabilities.
What users may notice
Additional checks can slow, pause or stop some legitimate tasks. ChatGPT and Codex users may be asked to review an action; API work can stop when monitoring detects potential misuse or unauthorised behaviour.
What buyers should ask
Security teams should separate defensive access from general model availability, document who can run agentic cyber tasks, and understand audit, monitoring, incident response and model-access controls before adoption.
HUBAI VIEWSecurity teams now need to evaluate the model and its operational controls as one procurement package.
Buyer decision signal: Critical cyber capability
What to verify next
1Approved cyber use cases
2Human authorisation boundaries
3Audit and task-stop behaviour
4Access tier and geography
5Incident escalation path
Read the evidence
Capabilities, availability and prices can change. HubAI keeps analysis separate from the underlying official material.
01OpenAI: GPT-6 Astra safety overviewOpen source ↗02OpenAI: GPT-6 Astra launchOpen source ↗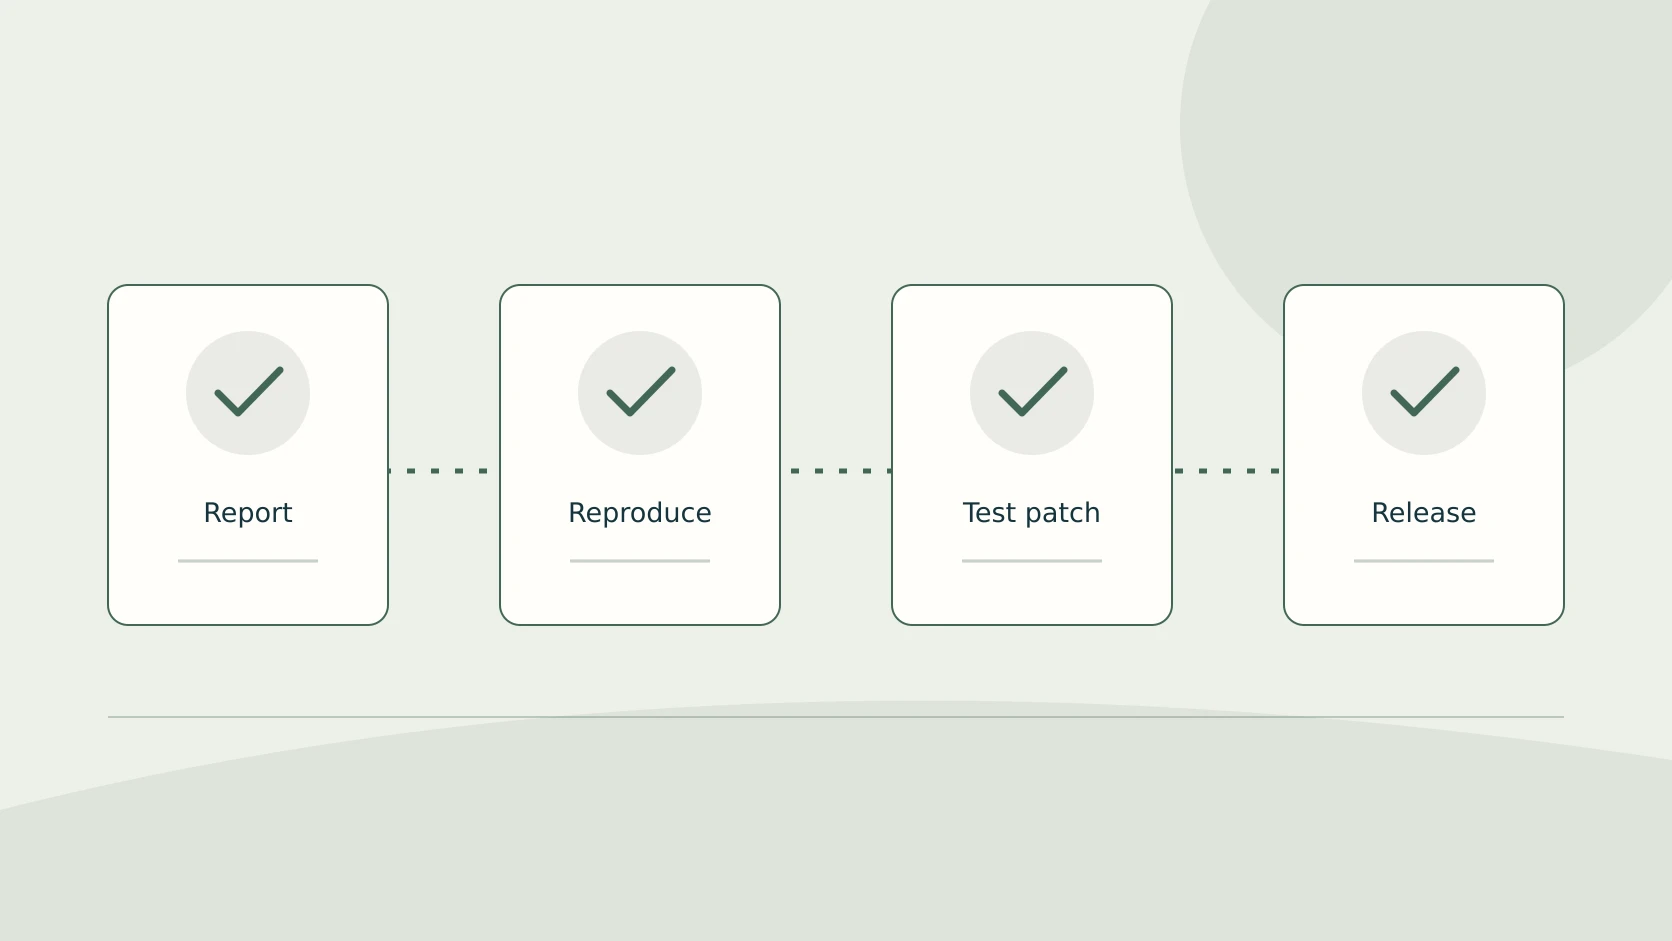 Safety
 Safety
 Safety
 Safety